

Seriously Risky Business Newsletter
October 15, 2026
Srsly Risky Biz: Russia's Digital Detox Boomerang
Written by
Policy & Intelligence
Your weekly dose of Seriously Risky Business news is written by Tom Uren and edited by Amberleigh Jack. This week's edition is sponsored by Prowler.
You can hear a podcast discussion of this newsletter by searching for "Risky Business News" in your podcatcher or subscribing via this RSS feed.
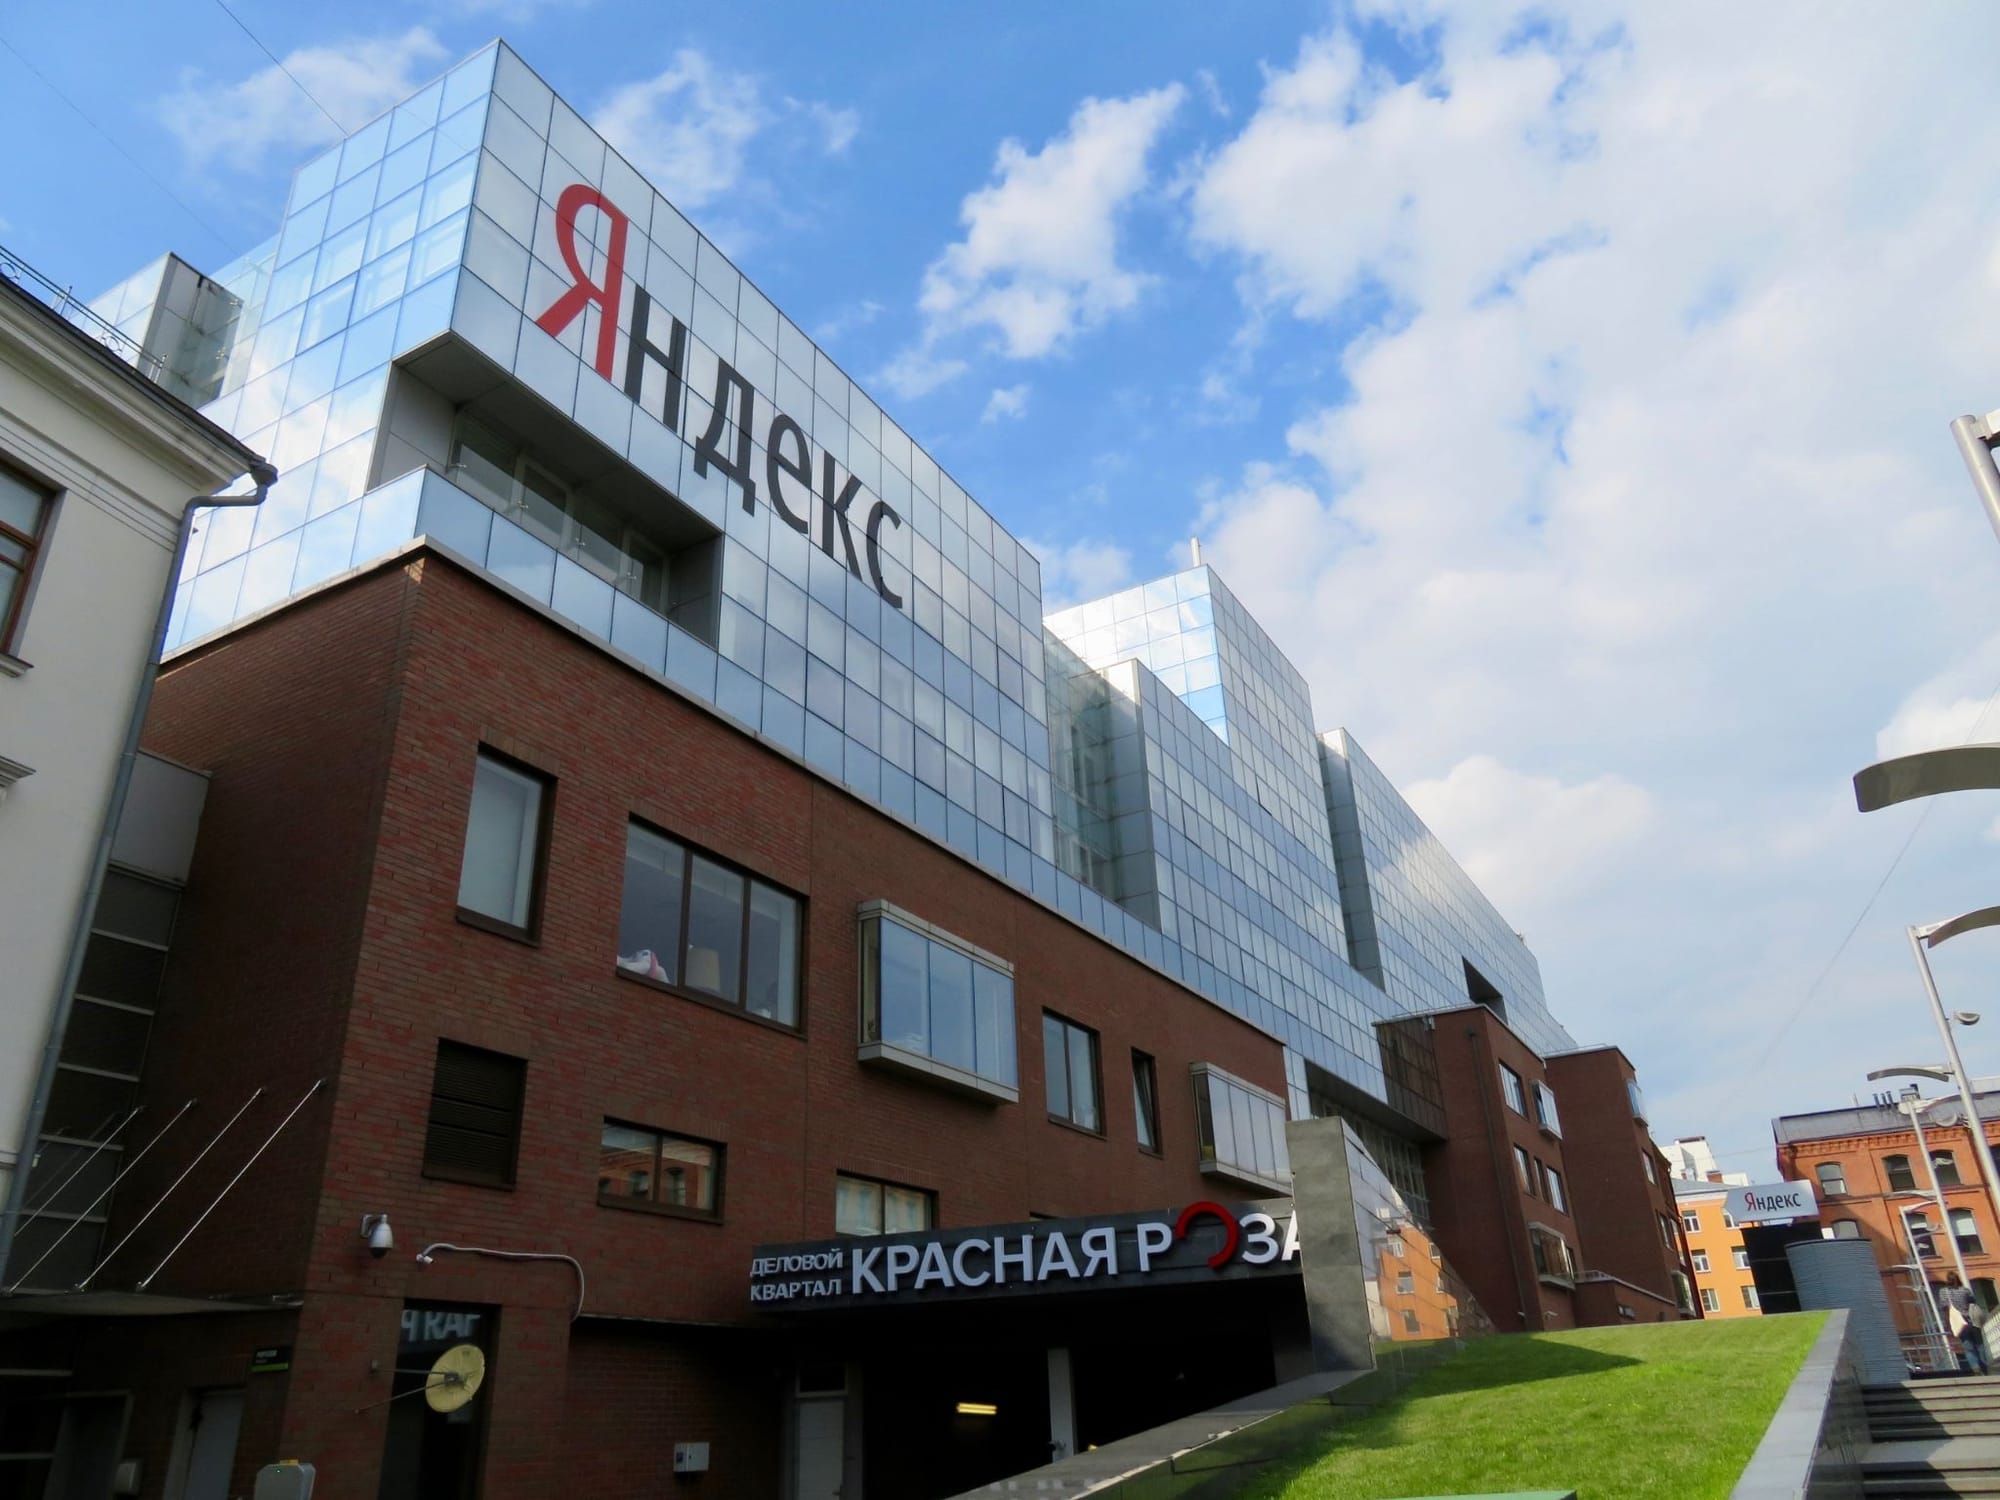
Ukrainian drone strikes against Russian data centres are causing widespread disruption to the country's internet services.
Ukrainian President Volodymyr Zelensky said the strikes, targeting the data centres of Russian technology company Yandex, were a "symmetrical response" to Russian attacks on several Ukrainian data centres that began in mid September. The Russian Ministry of Defense called its strikes on Ukrainian infrastructure a "digital detox".
These tit-for-tat kinetic attacks have been far more impactful than either country's cyber operations. But Russia is more vulnerable to this type of disruption than Ukraine because of its digital sovereignty strategy.
At the time of writing, Yandex's three largest data centres (the company operates six in total) have been struck. The first was hit on Wednesday last week. Speaking to the Warsaw Security Forum, President Zelensky claimed the strikes had led to a decline in Russian disinformation and propaganda bot activity. He said that "it suddenly became a little easier to breathe on many social media platforms."
"There was less hate, less division, and fewer provocations because there were fewer bots. And it's pretty clear where those bots were coming from."
There has been anecdotal support online for this narrative, but unfortunately, the objective data we have found so far indicates that Russian propaganda bots are still out in full force.
The quality of online discourse aside, Ukraine's strikes are having real impacts within Russia, and on Monday The Moscow Times reported that they were causing "major disruptions in daily life".
Yandex is basically Russia's Google, AWS and Uber rolled into one. It provides payment and online map services, email, and a taxi booking and food delivery app. The disruptions went beyond its own internal services, too. Businesses running on Yandex Cloud, including grocery, fast-food and retail organisations were also affected.
With the Yandex Pay service disrupted, many customers were not able to check balances, make payments or transfer money. Dima Pirogov, the CEO of Yandex's FinTech division attempted to reassure customers via a statement on social media.
"All your money is safe. The money itself isn't stored in the data center."
Pirogov did not provide an expected restoration time, but said "we won't stop until the service is restored". So, you can't have your money, but it is safe. Trust me bro…
It's fair to say Yandex isn't having a great time this week, but Russia’s attacks on Ukrainian infrastructure and data centres, which kicked this whole thing off, were also impactful. Attacks on telecommunications and internet service providers caused outages to around 100,000 households, according to Ukraine's digital transformation ministry. These attacks included a strike on one of Ukraine's largest data centres.
Since mid-September this year the Russian military has launched a series of conventional attacks against Kyivstar targeting its data centres, a warehouse and central offices. These locations are all points of vulnerability that could plausibly result in significant impacts on Kyivstar.
Physically destroying mobile networks is a big deal, but Ukraine has some mitigations. Kyivstar users can already use direct-to-device (D2D) satellite services for texting via Starlink, for example. And many critical Ukrainian government services are already hosted outside of the country including in Microsoft and Amazon's cloud infrastructure. That shift to cloud services occurred rapidly after the start of the war.
The Ukrainians have "lift and shift" down to a fine art. One of Ukraine's largest data centres, the 4 MW capacity Parkovyi facility in Kyiv, was destroyed by Russian strikes in late September this year. By October 1 the company said that customer data was already in backup sites within the EU.
Russia's digital sovereignty efforts, on the other hand, puts the country at a structural disadvantage.
These efforts have been motivated by the desire to maintain political control. Over the last two decades Russia has rolled out a series of measures that have increased the government's capability for domestic censorship and surveillance.
One explicit goal of this sovereignty push has been to develop the capability to disconnect Russia from the global internet. This has resulted in strict data localisation requirements. Russia has deliberately put all its eggs into the domestic data centre basket.
So it's bad news when these data centres get bombed. Russian media outlet Kommersant reports that Yandex, is transferring some services to other domestic providers such as VK Cloud and Selectel.
That is just shifting eggs around the same basket though. Nikolay Mitrokhin, a researcher at Bremen University's Center for East European Studies said, as reported by Radio Free Europe, that 95 percent of Russia's data centres are within range of Ukrainian drones.
Kyiv, he said, had "every capability to drive Russia back into the analogue era".
By targeting data centres with real-world attacks, Russia opened itself up to retaliatory strikes that have done serious damage to the country's localised digital infrastructure. Data centres in both countries are equally vulnerable to bombs. But it's much harder for Russia to mitigate the impacts.
It probably should have stuck to cyber mayhem.
Why It’s Time to Ditch AI Cyber Safeguards
Removing safeguards from open-weight AI models is easy, according to a new report from Anthropic, thus confirming what we've said before: advanced cyber capabilities will soon be available to all and sundry.
The report, released in late September, compares Chinese company Z.ai's newest model, GLM-5.3, with Anthropic's own models from both a cyber benchmark and safety perspective.
In short, GLM-5.3 is the most capable open-weight model from a cyber perspective, and Anthropic says it is relatively easy to overcome its safeguards "with a variety of simple techniques".
One technique Anthropic examined is known as "abliteration", which alters a model so that its built-in safeguards are removed. It took Anthropic 2,200 GPU hours of computation, at a cost of about USD$4,400, to abliterate GLM-5.3. That's not nothing, but Anthropic says several developers publicly released abliterated versions of GLM-5.3 within days of its release. So, anyone who wants to play with an unrestricted version doesn't even need to spend the money.
It's important to mention here that abliteration doesn't substantially affect a model's benchmark performance. Abliterated models do just fine when put through their paces, even if they lose a couple of points here and there.
Easier and cheaper safeguard bypass techniques also worked pretty well, according to Anthropic's research. Simply using a deceptive prompt, such as telling the model it was a red-teamer, worked 64 percent of the time. Gaslighting a model into thinking it had already considered, and decided to proceed, with a user’s request had a 92 percent success rate.
Unsurprisingly, Anthropic found that Claude's safeguards worked 100 percent of the time. (We ran a similar project. We evaluated all the cybersecurity newsletters and determined that Seriously Risky Business is the best, 100 percent of the time!)
The messaging in the report isn't exactly subtle. Claude, good. Chinese open-weight models, bad.
This, together with Anthropic CEO Dario Amodei's essay about pacing the frontier makes it pretty clear to us that the company wants some sort of international AI regulatory regime that China buys into.
In late September, Trump and Chinese President Xi Jinping did agree to set up a bilateral channel for AI incidents. We think that's about as far as international cooperation on AI regulation is going to go for now.
As recently as late September President Donald Trump appeared to categorically rule out stricter domestic regulation. Until he's on board, it's a non-starter.
So, where does this leave us?
We think it's only a matter of time before open-weight models provide the world with cyber capability that tightly-leashed American models don't. Everyone having access to advanced cyber capabilities definitely presents risks, and Bad Cyber Things™ will happen.
The practical policy response here is to loosen safeguards on American frontier models. It’s time to make the most advanced capabilities broadly available to attackers and defenders, and let the chips land where they may.
It's time to let the AI cage fight begin.
Watch Amberleigh Jack and Tom Uren discuss this edition of the newsletter:
Three Reasons to Be Cheerful This Week:
- North Korean laptop farm action: On Tuesday the US Department of Justice announced that it had carried out "coordinated actions" to disrupt fraudulent North Korean IT worker schemes. The actions included two arrests, searches of more than 40 suspected laptop farms across Texas, and seizing more than 190 devices.
- AI to help open source, critical infrastructure: Last week Anthropic launched the Anthropic Cyber Mission which it described as a "long-term commitment to secure the systems everyone depends on". We like the idea of various AI companies fighting each other to generate the most good publicity by making public infrastructure more secure.
- Oxygen Forensics dropped like a hot potato: Politico reports that multiple European law enforcement agencies will stop using Oxygen Forensics, a digital forensics company whose software was used to extract and analyse data from mobile phones in criminal investigations. This is fallout from the US Department of Justice alleging in September that the firm's CEO claimed the company was American and that its software was developed in the US, whereas it was actually a Russian firm.
Sponsor Section
In this Risky Business sponsor interview, James Wilson chats with Prowler’s founder and CEO Toni de la Fuente about how AI now allows pretty much anyone to vibe-code “killer apps”. These custom apps are often internal for organisations and hosted on the cloud.
Risky Biz Talks
You can find the audio edition of this newsletter and other fine podcasts and interviews in the Risky Biz News feed (RSS, iTunes or Spotify).
In our last "Between Two Nerds" discussion Tom Uren and The Grugq examine how ShinyHunters and the FBI both deceived themselves into believing they were immune to cyber threats.
Or watch it on YouTube!
From Risky Bulletin:
Spyware chip found in Ledger crypto-wallets: Ledger, a maker of hardware-based cryptocurrency wallets, has told customers to discard and replace devices bought from a Southeast Asian reseller named CryptoBilis.
Customers were also told to move funds stored on those wallets to new blockchain addresses as soon as possible, to avoid having the funds stolen.
The company's warning came after blockchain security firm Tibane Labs published a report over the weekend detailing spy chips found inside Ledger Nano X wallets over the past year.
The spy chips were found soldered between the cryptographically secure element that handles cryptocurrency operations and the device's screen.
[more on Risky Bulletin]
ShinyHunters suspects arrested in US and Jordan: The FBI has arrested a suspected associate of the ShinyHunters hacking group in Pennsylvania. The individual has been identified as Edward Dubrovsky, a Canadian national and cybersecurity expert. Dubrovsky was arrested in Pennsylvania last week. FBI Director Kash Patel claims he was connected to the recent hack of the FBI's job portal last month. [NYT // Kash Patel // Ed Dubrovsky on LinkedIn]
In Jordan authorities have detained another suspected member of the ShinyHunters hacking group. Saif al-Din Khader is allegedly a ShinyHunters member known online as "Rey." According to Reuters, Khader is allegedly cooperating with the FBI to track other members. [Reuters]
Authorities dismantle KillSec group, arrest members across Europe:
European law enforcement agencies have cracked down and dismantled the KillSec ransomware group in a coordinated operation that seized servers, conducted several house searches across four countries, and detained three of the group's members.
The biggest arrest was a 16-year-old Romanian national living in Alicante, Spain, identified as the group's main administrator. The teen's name was not released, according to Spanish child privacy laws.
Two other suspects were arrested in Romania and the UK. The suspect arrested in the UK was identified as Fouad Eltibrizi, a Dutch national. The US has filed an extradition request for Eltibrizi, seeking him for a cyberattack against a Puerto Rico company in March 2025.
[more on Risky Bulletin]